

NFC Proof
iOS and Android
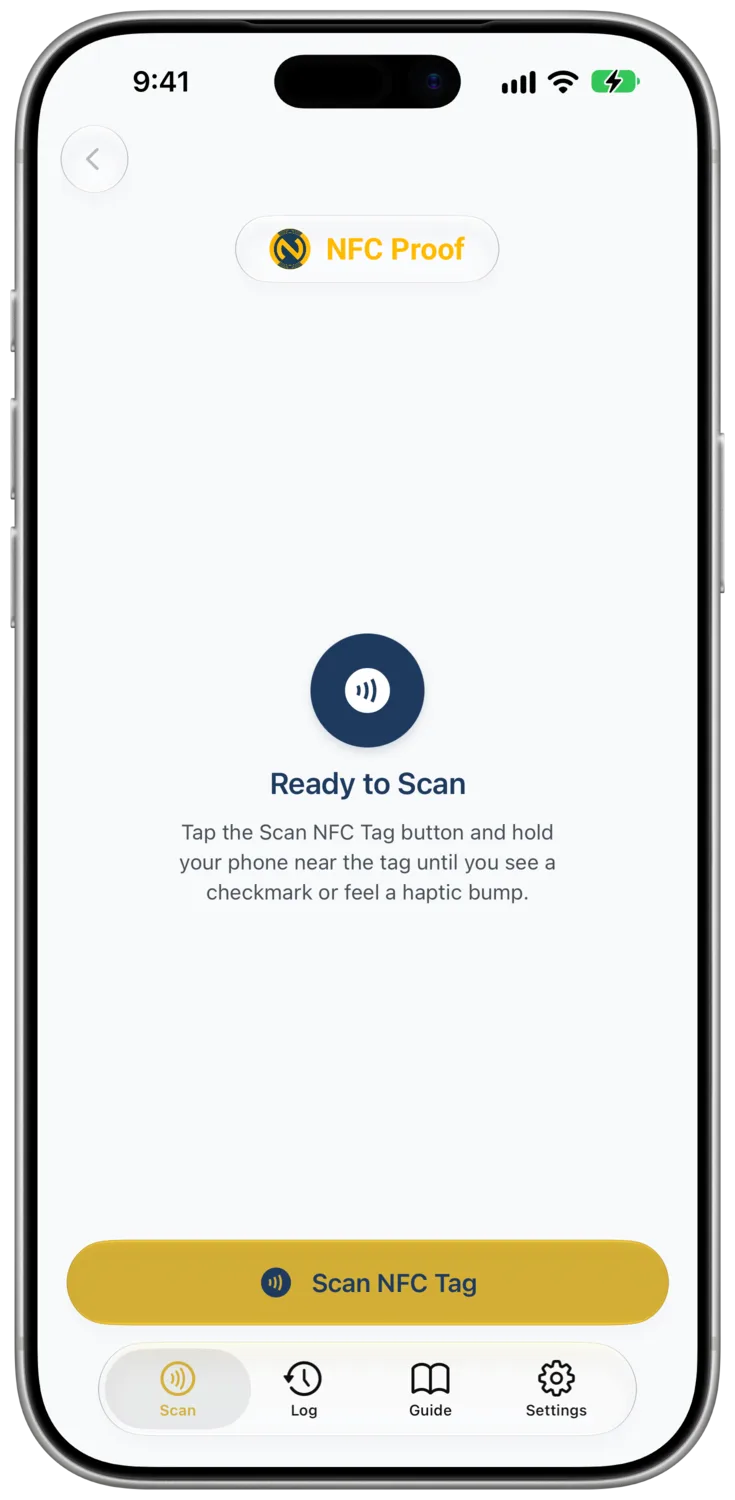
The free NFC Proof app checks any of our tags and keeps a scan log for your collection. It also verifies the chip's NXP factory signature on your device, a check a browser cannot do.
We mint NFC tags that generate a fresh code with every tap. Tap one with an NFC-enabled phone to open our validation service in your browser. It checks the code, accepts it only once, and shows the tag's recorded product details and scan counter. You need no app. NFC Proof also verifies the chip's NXP signature. A valid result authenticates the tag. It does not prove the attached item is genuine.
https://validate.nfcmint.com/?uid=04A1B2C3D4E5F6&ctr=000006000007&cmac=8F3A1C2D9E4B7F60D07B45E91AC8362F
 NFC Proof
Validating Tag
Replay Detected
Valid Tag
Example Trading Card
Counter
We use the same chip and validation service for collectible cats, permanent public records, and private tamper evidence.
Collect our cats and tap them at real places around the world to earn virtual passport stamps. The app checks your location before it adds a stamp.
Visit StampCatsMakers write a permanent public record once in OnceMark. Anyone who scans sees a genuine tag and the record, word for word, with no name attached.
Visit OnceMarkIf you sell collectibles, activate a seal in TamperKit before shipping and check it on return. Keep evidence for a marketplace dispute.
Visit TamperKitStampCats collectibles, OnceMark tag packs, and TamperKit seal packs ship from our Amazon storefront.
How It Works
Three things happen, in about a second, and you can watch all of them. There is no account, no reader, and no special phone.
Step 1
Hold your phone near the tag. Your phone opens a web page. There is nothing to install and nothing to sign up for.
Step 2
The chip writes a fresh single use code into that link every time it is read. It never repeats itself.
Step 3
Our service checks the code and tells you plainly whether it is genuine, already used, or not one of ours.
Apps and Tools
Choose an app to check a tag, configure NFC chips, create permanent records, document seals, or collect travel stamps.
iOS and Android
The free NFC Proof app checks any of our tags and keeps a scan log for your collection. It also verifies the chip's NXP factory signature on your device, a check a browser cannot do.
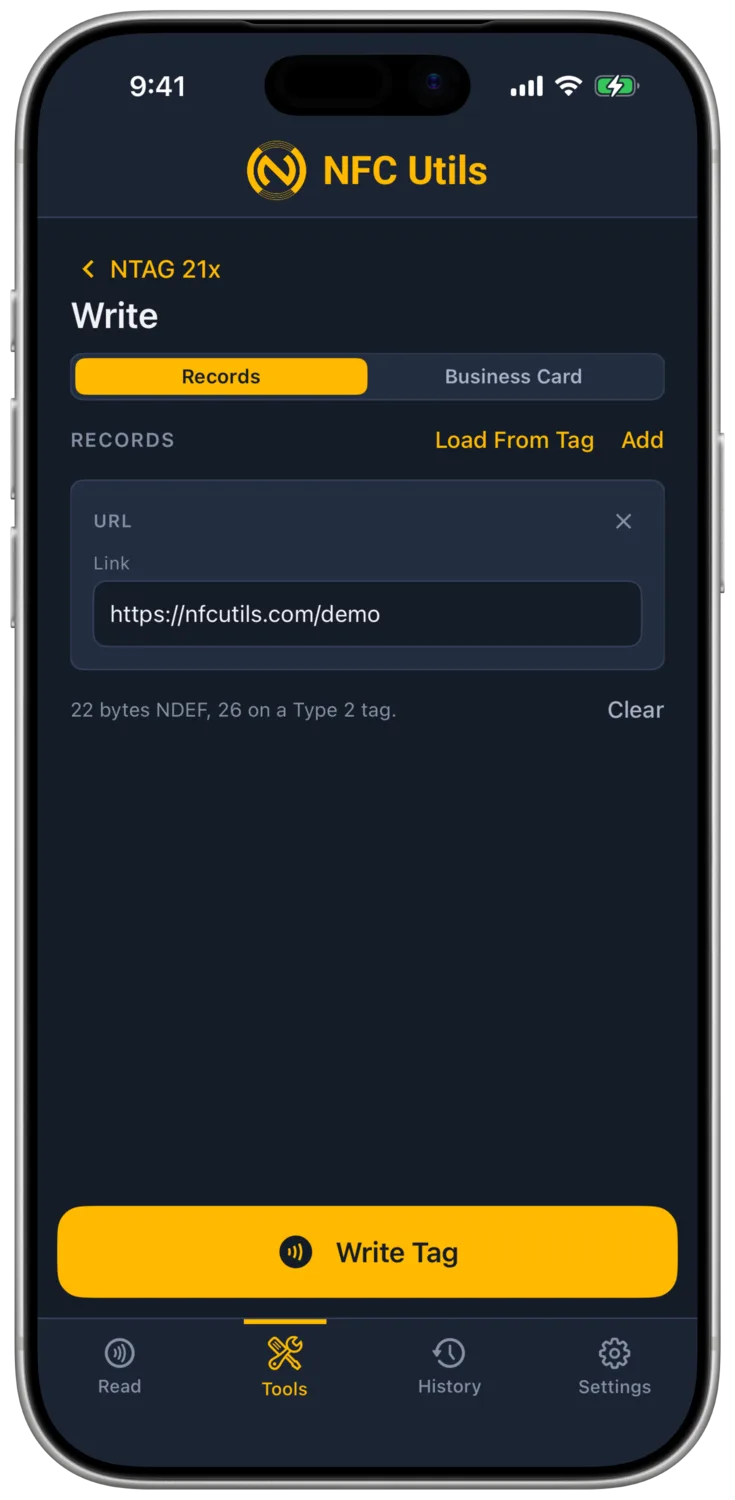
iPhone, iPad, Mac, and Android
Read, write, and configure NFC tags. Follow practical tutorials for supported chip families, connect a reader, and explore the full guide.
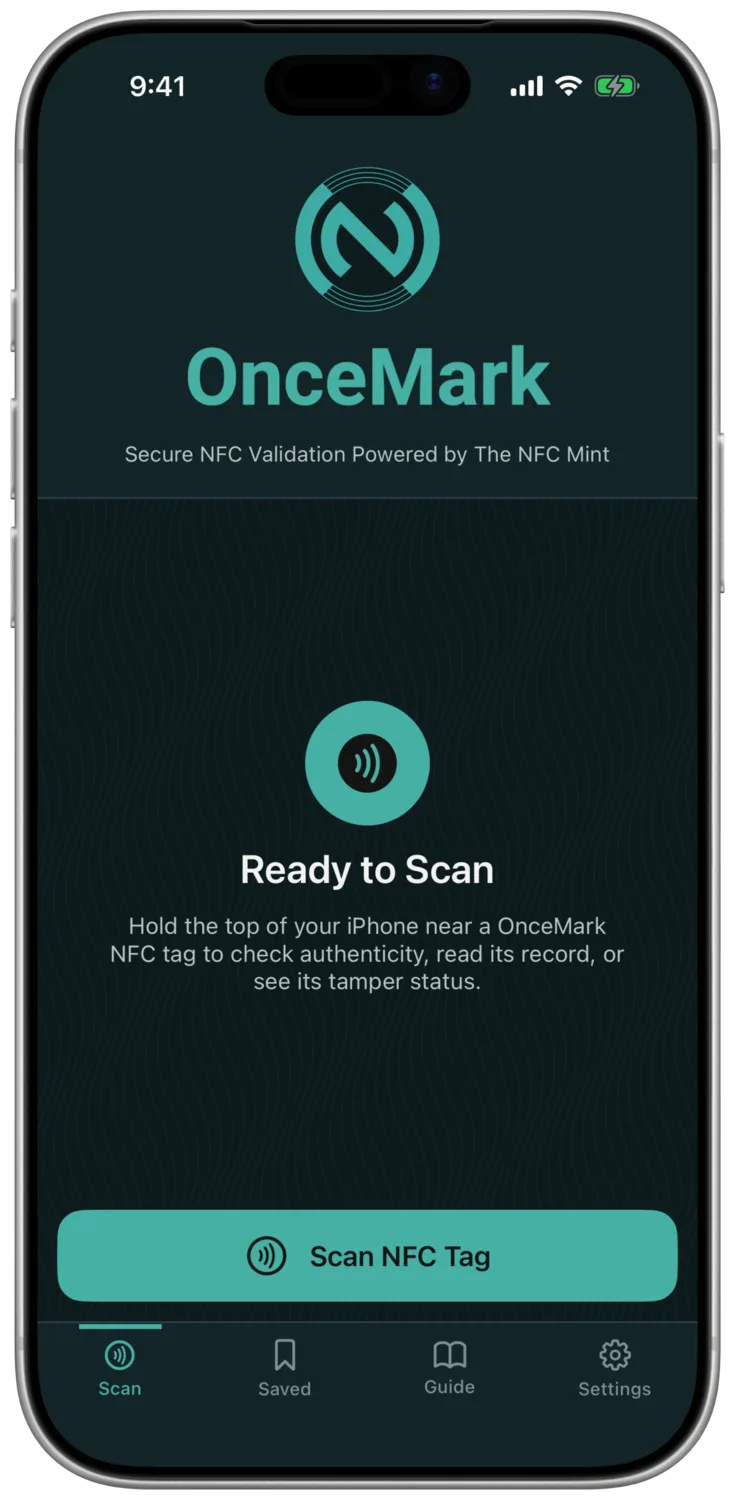
iOS and Android
For makers and small brands. Write your product's record onto its tag once, permanently. Anyone who scans sees a genuine tag and the record you wrote, shown word for word with no name attached.
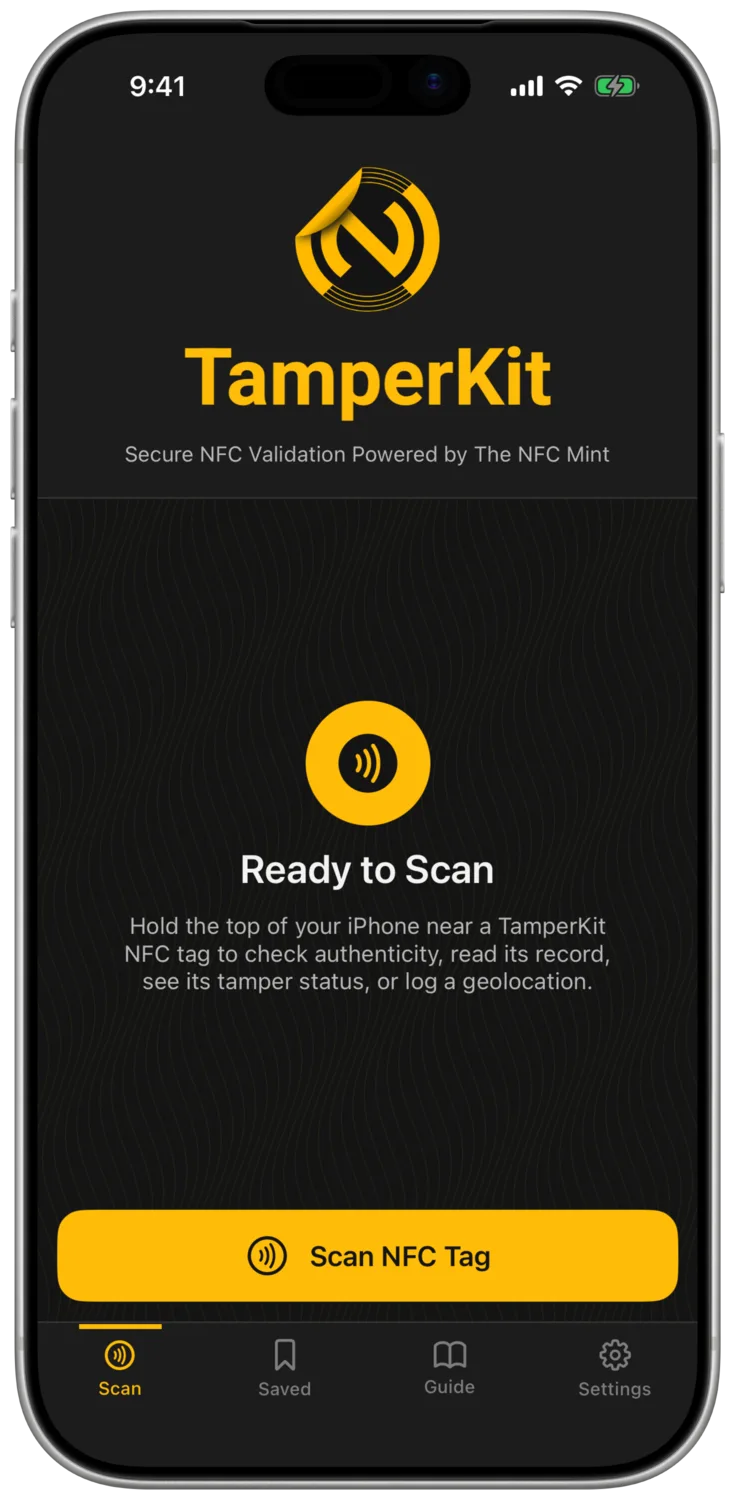
iOS and Android
Sellers use TamperKit to document seal openings, locations, and scans. Export a cryptographic proof of the evidence chain, including photo hashes, to help combat return fraud or show the seal read intact on arrival.
iOS and Android
Tap your cat at places around the world and collect stamps in its virtual passport. Location is checked, so the stamps mean you were really there.
A hardware security module holds our master key and derives each tag's key from it and the tag's UID. We write that key into the chip once at our facility. It passes through our encoding software in memory, is never stored in a database, and cannot be read back from the chip.
Every tap produces a signed message that has never been produced before. That is the whole design, and the details are worth reading if you want them.
A genuine tag proves the tag is genuine. It does not prove the tag is still attached to the item it was applied to, and it does not inspect the item. A tag is also a bearer instrument, so whoever holds it can tap it. We build the seals, the counters, and the records to make misuse visible, and we tell you plainly where the boundary is.
From the Articles
The deep material lives in the articles, written so any paragraph stands on its own. These two are the place to start.

NFC Proof
Two products, identical to the eye. How anyone with a modern phone can tell them apart in about a second, with no training and no app.
Read the Article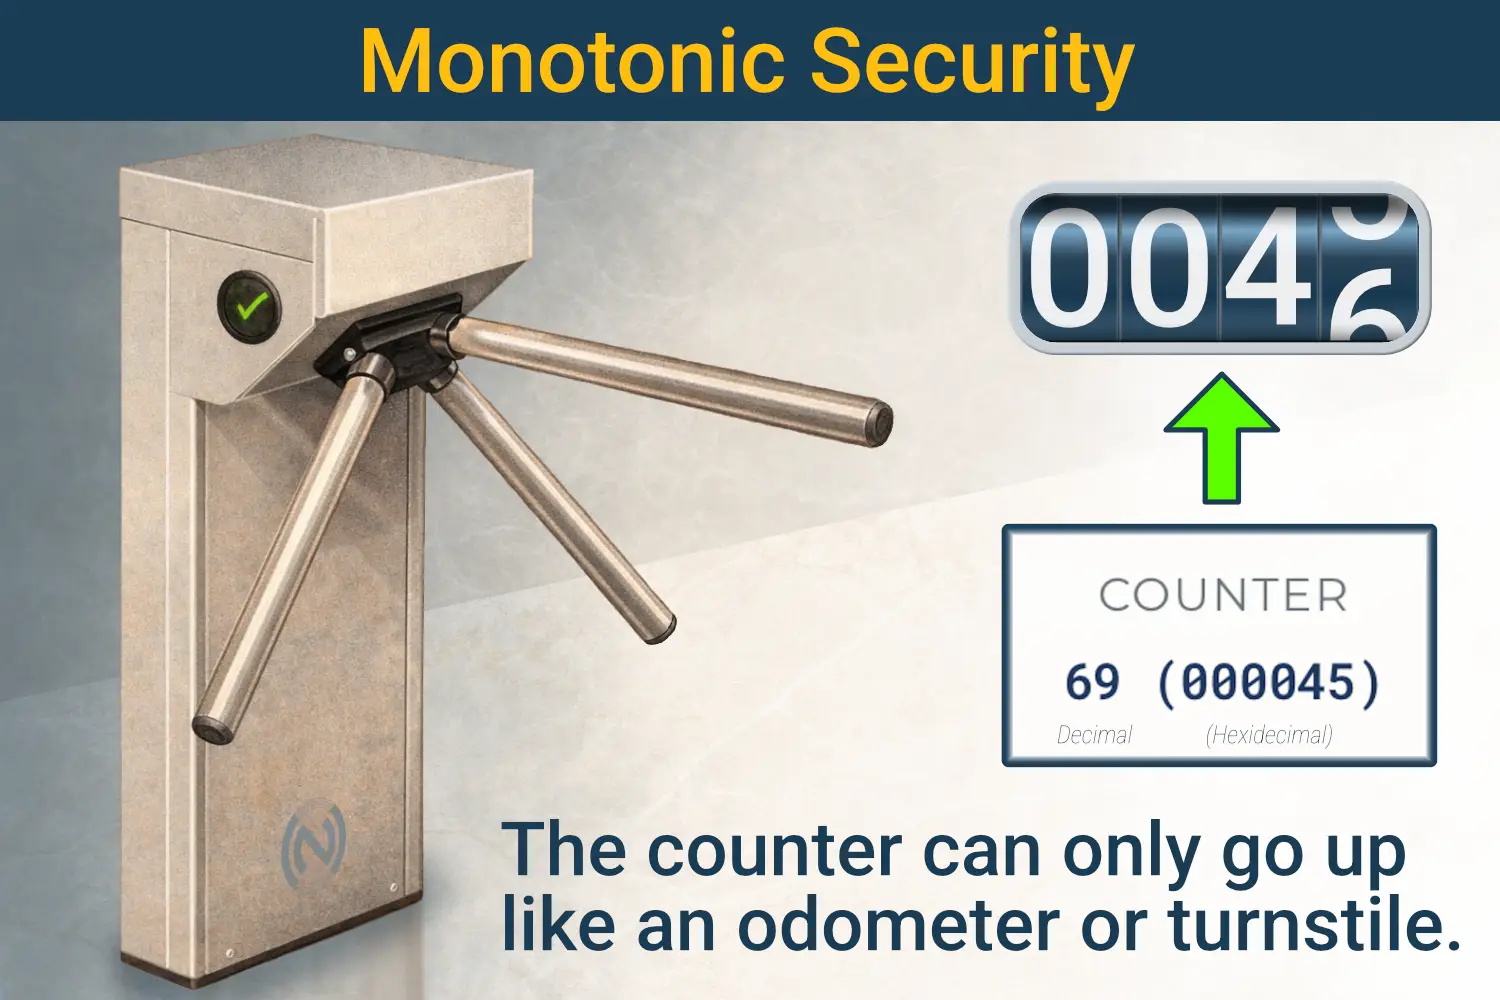
NFC Proof
Why a counter that only moves forward defeats copied links, and what the chip signs on every single read.
Read the ArticleThe NFC Mint has no user logins. Not on this site, not in our apps, and not behind the scenes. There is no account to create, so there is no password to steal, no email list to breach, and no profile of you accumulating anywhere. Where an app needs a credential, your device generates a random secret and our server keeps only its hash. A key identifies an app install, never a person.
We do not fulfill our own orders, and that is deliberate. Tags ship through our Amazon storefront, so your name and shipping address go to the fulfillment intermediary and never enter our systems. We chose a smaller attack surface over a customer list. A database we never build is a database nobody can breach, subpoena, or sell.
What we mint are bearer instruments. A tag proves that something is valid or that something happened, and whoever holds it holds the proof. Everything beyond that verdict is opt-in. A maker chooses what a public OnceMark record says. A seller chooses when a private TamperKit record is disclosed, and until then a stranger's scan shows only that the tag is genuine and activated.
We state the boundary plainly. Like nearly every web service, our servers log IP addresses and user agents on each scan, and we use them for one purpose, stopping abuse such as replayed scans and rate flooding. Those service logs are deliberately kept outside the evidence records and outside the anchored history, so they never become part of any proof and can be purged without breaking one. The record layer stores no identity at all. We exist to protect consumers from fraud, not to watch them.
Get help with your tags and apps, understand a scan result, or ask about our products.
Already have a tag, a seal, or one of our apps? Write to us and a person will answer.
Ask us about StampCats collectibles, OnceMark tags, or TamperKit seals.
Result Help on the validation service already answers most of what people write in to ask.